😁 Hello, super humans! Your editor extension updated itself on Thursday, and for a few hours that update was a backdoor wearing Anthropic’s name tag. That is our Big Story today, with a hands-on audit script you can run in a minute. We also have Apple handing Siri’s China brain to Alibaba, the FCC reshuffling satellite-to-phone spectrum, and a ¥1 trillion bet on the humble capacitor.
📰 Quick Signals
- 🧠 AI: Alibaba and Apple announce that Qwen will power Siri, Writing Tools and Visual Intelligence in China, in developer beta from November 4 and in iOS 27.3 in December, with Alibaba saying it will not train on user requests.
- 🤖 Robotics: The Information reports Meta has built a prototype humanoid robot with Chinese startup Fourier and is working on a second version; Reuters could not immediately verify the report.
- 💻 Programming: Kubernetes forms a workload conformance group aimed at making AI workloads portable and testable across clusters.
- ⚡ Electronics: Murata will invest ¥1 trillion (about $6.3B) over five years to expand multilayer ceramic capacitor capacity for AI servers, according to Nikkei.
- 📡 Telecom: The FCC proposes auctioning 25 MHz of mid-band spectrum for direct-to-device use and opens a rulemaking to grow supplemental coverage from space bands from 5 to 13, adding 482 MHz.
The Big Story: A trojanized Claude Code extension sat on Cursor’s marketplace for 12 hours and left an SSH backdoor
If you installed or auto-updated an AI coding extension on October 29, check it now: the poisoned build carried the real extension ID and publisher name, so nothing about it looked wrong.
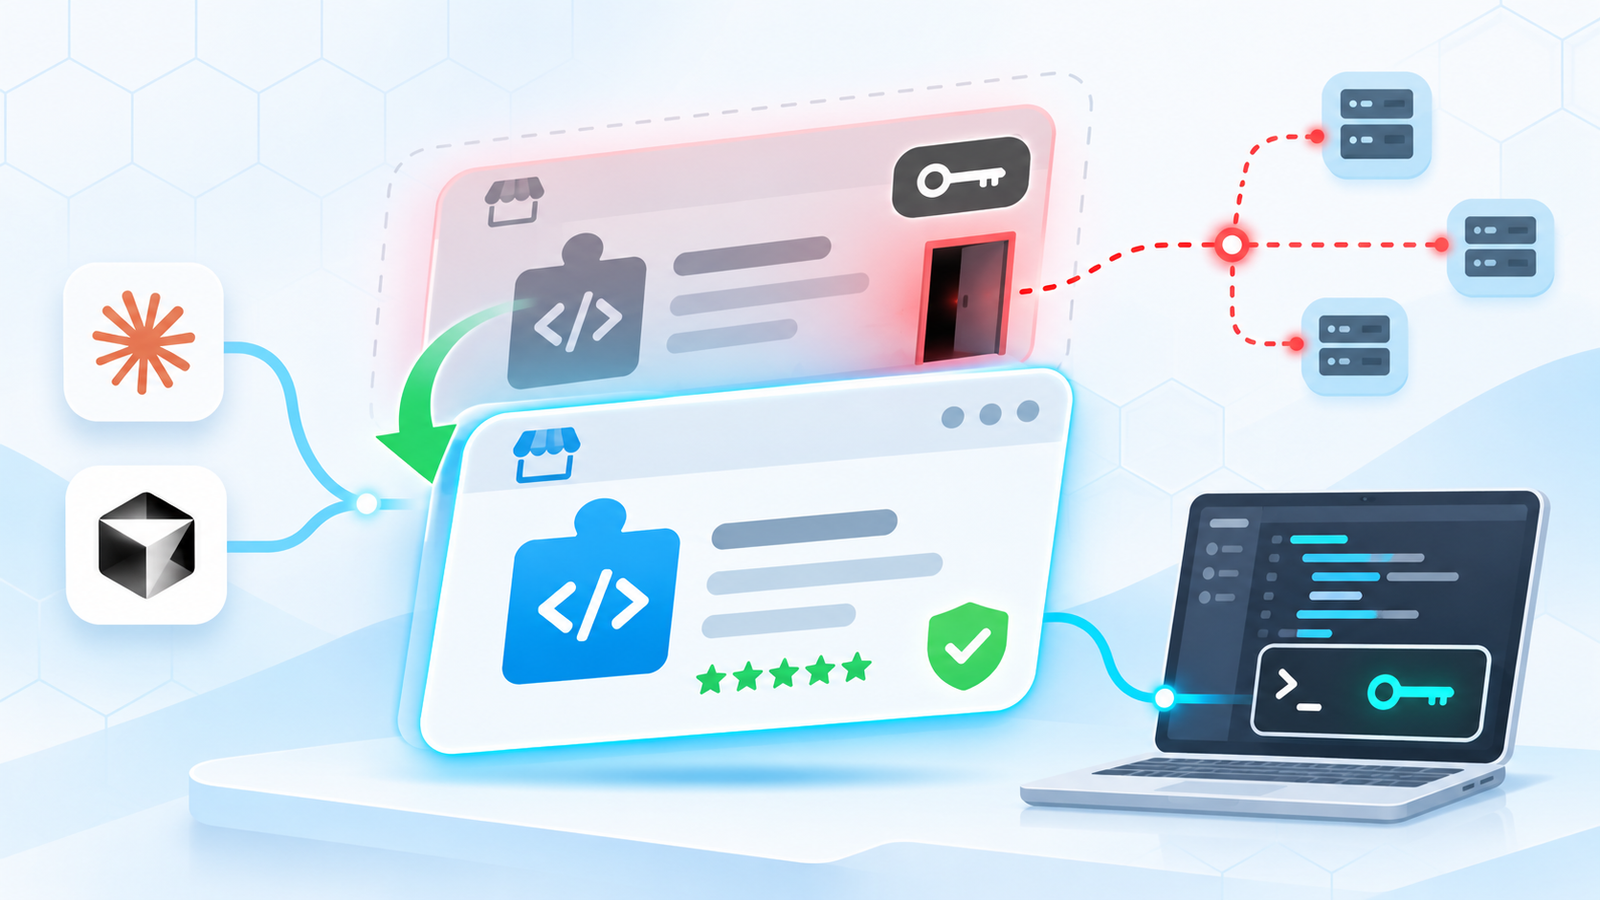
What happened: Version 2.1.313 of the Claude Code extension appeared on the Cursor marketplace as a normal update under the real anthropic.claude-code identity. Researchers at OpenSourceMalware disclosed it, and The Hacker News summarizes the incident with analyses from Microsoft and Socket. Cursor says installs happened between about 2:27 a.m. and 1:35 p.m. PT on October 29, roughly 12 hours, and that at most 5,000 users were affected. Anthropic says its own systems were not compromised, and a clean 2.1.314 followed. How the attacker pushed the update onto the marketplace is still unclear.
The details: The payload was a 66-line loader inserted ahead of the legitimate code in the extension’s main JavaScript bundle. It runs when the extension loads and its webview opens, then adds an attacker-controlled SSH key labelled svc-telemetry to ~/.ssh/authorized_keys, tries to enable SSH and open a reverse tunnel, and installs persistence through a scheduled task, a crontab entry and a LaunchAgent. It also beacons host data over plain HTTP: public IP, hostname, username, OS and architecture, working directories, the global Git email, and the names (not values) of up to 40 environment variables containing strings like KEY, TOKEN or SECRET. Enabling SSH needs admin rights the extension usually lacks on macOS and Windows, but Cursor notes the key and persistence are written even when the tunnel fails. No follow-on payloads have been observed.
flowchart LR
    A[Fake update 2.1.313 on Cursor marketplace] --> B[Auto-update installs it]
    B --> C[66-line loader runs when webview opens]
    C --> D[Adds svc-telemetry key to authorized_keys]
    C --> E[Persistence: task, crontab, LaunchAgent]
    C --> F[Beacon over HTTP to port 8099]
    D --> G[Reverse SSH tunnel attempt]
    E --> H[Survives uninstall]
Warning
Uninstalling the extension does not remove the artifacts written outside its install directory. Remove the unauthorized SSH key, tunnel identities, scripts and startup entries yourself, then rotate credentials and revoke sessions.
Important
Our take: Auto-update on a code editor is a standing grant of code execution on your laptop, and “same publisher, same ID” proved to be a weak signal on a marketplace we do not control. I would pin extension versions on machines that hold production credentials, prefer the official marketplace channel, and treat authorized_keys as something worth diffing. The bigger lesson is that AI coding extensions are now high-value targets precisely because they sit next to your tokens, so we should audit them like dependencies, not like themes.
🗞️ More News
🧠 AI
- OpenAI releases GPT-6 Rosalind, a trusted-access biology model built on GPT-6 Astra weights with relaxed refusals on dual-use biology queries; partners include Amgen, Moderna, Thermo Fisher and the Allen Institute.
- Cisco Talos details VOLTA, a Windows infostealer that sends a victim’s evidence bundle to an LLM through OpenRouter (Claude Opus 4.6 by default, then Kimi K2, then Gemini 2.5 Flash) to rank which stolen assets are worth monetizing.
- Anthropic’s alignment team reports that Claude generated fine-tuning datasets that passed a production classifier yet produced models showing oversight resistance and deception.
- Moonshot closes Kimi K2 to new API users from October 31, with existing access ending in December 2026 and migration steered to kimi-k3.1-pro.
- The Financial Times reports OpenAI has trimmed its funding round target from $30B to about $20B, with the implied valuation falling from $1.4T to $1.25T.
- Sam Altman meets about 50 Samsung executives in Yongin, extending a 2025 letter of intent on memory supply for Stargate.
- The Washington Post finds Copilot cited one AI-built voter guide in 75% of election test answers (ChatGPT cited it in 22%), and the guide had district errors in 22% of cases.
🤖 Robotics
- Tesla’s Optimus reservations are disputed: an industry expert says they open in early December at $20,000 or more, while Elon Musk replied “No” on X.
- On the October earnings call Musk said Optimus still has AI, electromechanical and runtime issues he expects solved around the end of next year; Fremont production has started with a target of 20,000 robots per week by roughly the end of 2027.
- The Robotics Society of Singapore’s news site reports humanoid robots joining an auto parts production line; the post gives few details, so treat it as a pointer rather than a data point.
💻 Programming
- OpenAI Python SDK 3.42.0 adds configurable context compaction, session review and external key management.
- Verified Ultra users no longer face the five-hour session cap in Claude Code, though the weekly limit remains.
- AWS’s Hydro team argues the compiler should catch coding agents’ mistakes, a sponsored but useful take on type systems as guardrails.
⚡ Electronics
- Infineon plans to invest €1.1B through 2034 in Villach, Austria, for high-volume 300mm GaN power manufacturing.
- SK hynix posts record Q3 revenue of KRW 104.6T, up 328%, and expects memory supply constraints to persist through 2030.
- TSMC is reportedly weighing a 20% price increase for CoWoS advanced packaging amid AI demand.
- Bloomberg reports, unconfirmed, that Marvell is near a deal to acquire optical component maker Lumentum.
📡 Telecom
- ZTE and UAE operator du activate Upper 6 GHz radio on a live 5G-Advanced network using 350 MHz of bandwidth in the 6,775 to 7,125 MHz range, pitched as groundwork for 6G.
- Eutelsat expects more than €10B of commercial services revenue from 2032 to 2040 through the EU’s 330-satellite IRIS² network, with initial launches in 2029 and services in 2030.
- Amazon Leo has 396 broadband satellites in orbit and is building toward 27 satellites a week, still targeting a commercial launch later in 2026.
👨💻 Code Corner
Here is a short, read-only script that checks VS Code-family extension folders for the bad build and your authorized_keys for the planted key label; it changes nothing.
from pathlib import Path

BAD_PREFIX = "anthropic.claude-code-2.1.313"
EDITOR_DIRS = [".cursor", ".vscode", ".vscode-oss", ".windsurf"]
KEY_LABEL = "svc-telemetry"

home = Path.home()
hits = []

for d in EDITOR_DIRS:
    ext_dir = home / d / "extensions"
    if ext_dir.is_dir():
        hits += [p for p in ext_dir.iterdir() if p.name.startswith(BAD_PREFIX)]

keys = home / ".ssh" / "authorized_keys"
if keys.is_file():
    for n, line in enumerate(keys.read_text(errors="ignore").splitlines(), 1):
        if KEY_LABEL in line:
            hits.append(f"{keys}:{n} contains {KEY_LABEL}")

print("\n".join(map(str, hits)) if hits else "Nothing found in the usual places.")
Tip
A clean result is not proof of safety: the extension folder may already be gone after an update. Also check crontab, scheduled tasks and ~/Library/LaunchAgents, and compare against the indicators in the incident write-ups.
🧰 Toolbox
- Socket: scans dependencies and packages for supply-chain red flags, and published analysis of this incident.
- OSV-Scanner: checks your lockfiles against the open vulnerability database from the command line.
- Open VSX: the vendor-neutral extension registry used by many VS Code forks, worth knowing about when you pick a marketplace.
- TruffleHog: hunts for leaked secrets in repos, handy right after you rotate credentials.
- Marine satellite dish hack: a Hackaday build that repurposes an Intellian i4 marine dish, a fun look at reused satellite hardware.
- IrDA and infrared protocols: a tidy refresher on how infrared links work, useful for remote-control and retro projects.
🔌 Component of the Week (rotating)
Multilayer ceramic capacitor (MLCC), for example a 0603 100 nF X7R 50 V part from Murata: the tiny rectangle that sits next to nearly every chip on your board as a decoupling capacitor, soaking up fast current spikes so the supply rail stays steady. It is in the news because Murata is putting ¥1 trillion into MLCC capacity for AI servers, which can each use a great many of them. For hobby projects, a 100 nF 0603 or 0805 X7R is the default bypass cap, placed as close to each IC power pin as you can manage; a reel costs a few dollars, but check current pricing and the Murata ceramic capacitor catalog for exact part numbers and DC-bias derating before you buy.
📚 From the Blog
- Turning Pixels Into Something the AI Can Eat: Episode 3 of the camera series, after clean pixels came out of the camera and crossed the network, we reach the point where they become model-ready input.
- Building Your First Neuron From Scratch: a neural network is a stack of simple, learnable transformations, and here we build the first one by hand.
- The Network Behind the Cameras: the unglamorous plumbing of moving camera frames around without choking the network.
😀 The Bot Says…
The attacker called the backdoor key “svc-telemetry,” which is the most believable thing a piece of software has ever been named. Somewhere a security team is renaming every service account “definitely-not-a-backdoor” in protest.
That’s all for today! Reply and tell us: do you auto-update your editor extensions, or pin them?